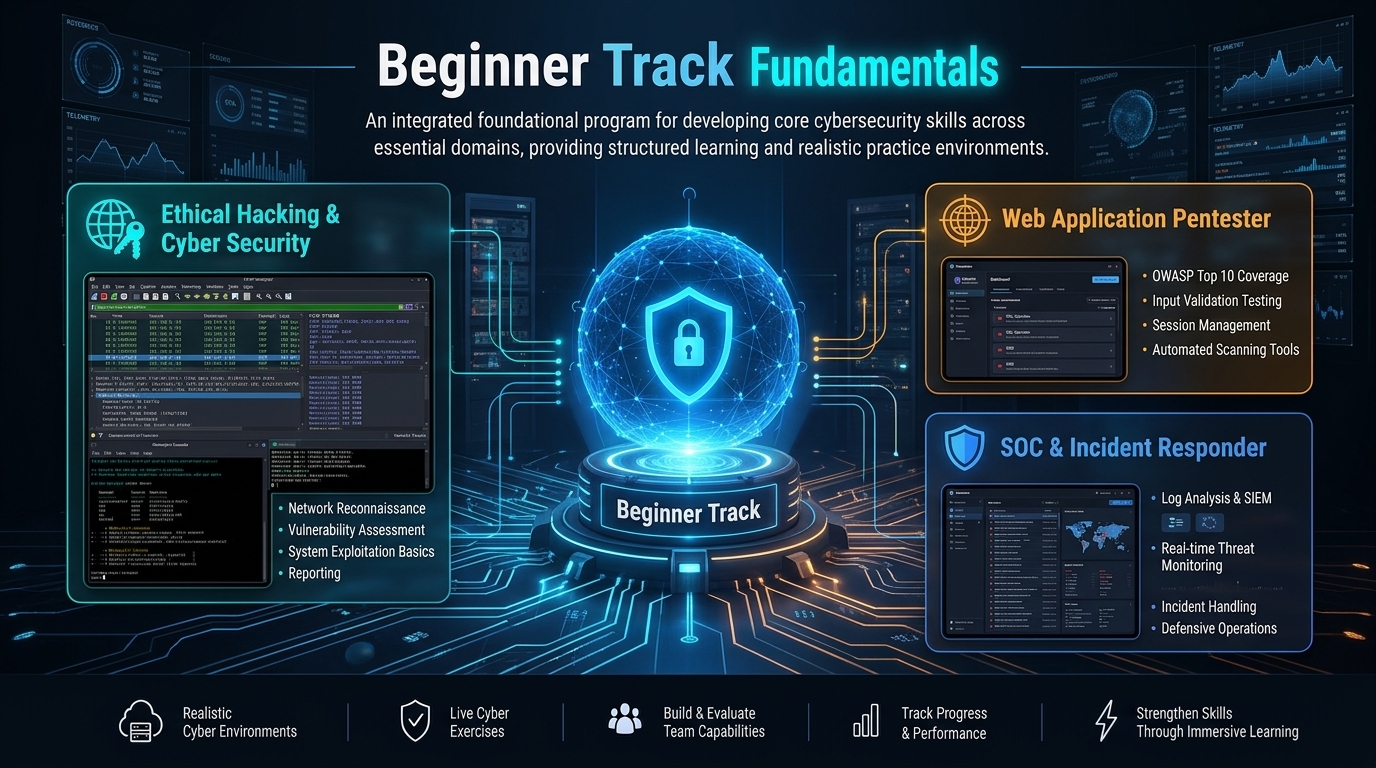
Beginner Track: Foundational Cybersecurity & Defensive Operations
Kickstart your cybersecurity career with hands-on practice labs, structured learning paths, and real-world tools. Built for aspiring security analysts, ethical hackers, and defensive responders.
Zero-Install Browser Labs
Launch full Linux and security terminal environments directly in your web browser.
Industry-Standard Tools
Practice with real tools including Nmap, Wireshark, Burp Suite, and terminal utilities.
Guided Career Roadmaps
Step-by-step beginner curriculums taking you from networking basics to active defense.
Verified Skill Badges
Earn course completion certificates and practical skill credentials as you finish labs.
Ethical Hacking & Cyber Security
Master core ethical hacking fundamentals, network protocols, reconnaissance methods, and vulnerability discovery across realistic practice environments.
Linux & SSH Practical
Master essential Linux terminal commands, remote SSH shells, and system permission security.
Network Traffic Analysis
Capture, inspect, and analyze live HTTP and FTP packets using Wireshark analyzers.
Password Testing & Hydra
Execute structured brute-force authentication assessments against insecure service daemons.
Reconnaissance & OSINT
Learn automated subdomain discovery, Google dorking syntax, and vulnerability reporting standards.
Web Application Pentester
Learn to identify, test, and exploit top web application security flaws following the OWASP Top 10 framework using industry-standard tools.
OWASP Top 10 Exploitation
Hands-on practice targeting SQL Injection, Cross-Site Scripting (XSS), and broken access controls.
Authentication & Session Flaws
Test insecure session cookies, password reset logic, and user impersonation vulnerabilities.
Burp Suite Request Interception
Master HTTP proxying, request tampering, automated fuzzing, and parameter analysis.
Vulnerability Reporting
Document reproducible proof-of-concepts, CVSS severity ratings, and remediation steps.
SOC & Incident Responder
Step into the shoes of a Security Operations Center analyst to monitor enterprise network traffic, investigate alerts, and respond to incoming incidents.
Cyber Defense & Kill-Chains
Map attacker tactics to the MITRE ATT&CK framework and understand threat actor lifecycles.
Log Analysis & Threat Detection
Inspect authentication, system, and web server logs to identify suspicious intrusions.
SIEM Incident Investigation
Correlate security telemetry, investigate endpoint alerts, and triage attack indicators.
Incident Containment Playbooks
Execute standardized containment procedures to isolate compromised hosts and eradicate threats.
Frontlines Says.