Adversarial Attack Simulation & SOC Defense Validation
Validate your organization’s cyber resilience through authentic Red vs Blue warfare and collaborative Purple Teaming exercises. Hacktify’s Red-Blue Teaming Platform bridges the gap between offensive realism and defensive readiness, allowing security teams to emulate sophisticated Advanced Persistent Threat (APT) campaigns, stress-test SIEM/EDR detection rules, and fortify enterprise incident response playbooks.
- MITRE ATT&CK Aligned Scenarios: Realistic adversary emulation spanning initial access, lateral movement, privilege escalation, and exfiltration.
- Real-Time Attack-Defense Telemetry: Measure blue team Mean Time to Detect (MTTD) and Mean Time to Respond (MTTR) against live offensive strikes.
- Automated & Manual Campaign Execution: Run automated adversary emulation chains or conduct fully manual red team intrusions in isolated network environments.
- Teaming Collaboration Hub: Transparent exercise dashboards enabling red and blue teams to deconflict alerts, share IoCs, and optimize defenses in real time.
1,500+ TTPs & 30+ APTs
Deep offensive-defensive coverage emulating real-world state-sponsored threat groups and full attack chains.
Attack Detection & Auto-Scoring
Automated telemetry engine: Blue team detection logs validate defense while Red team gains points for offensive execution.
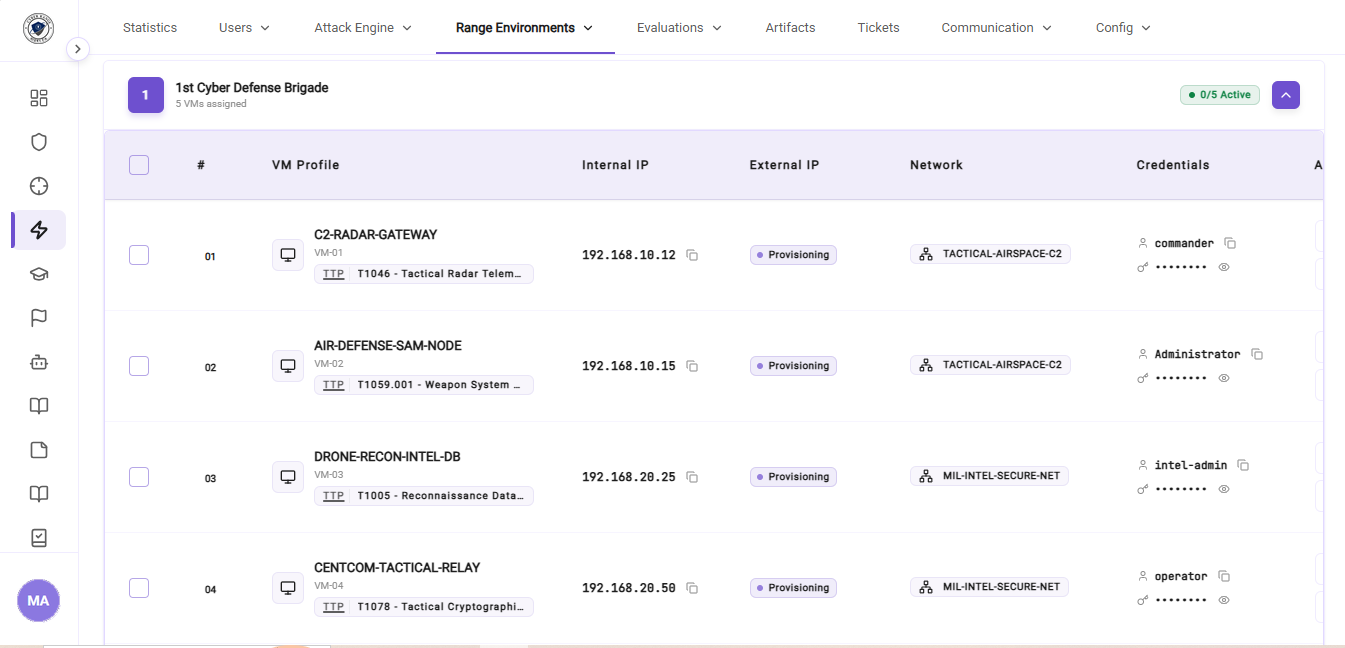
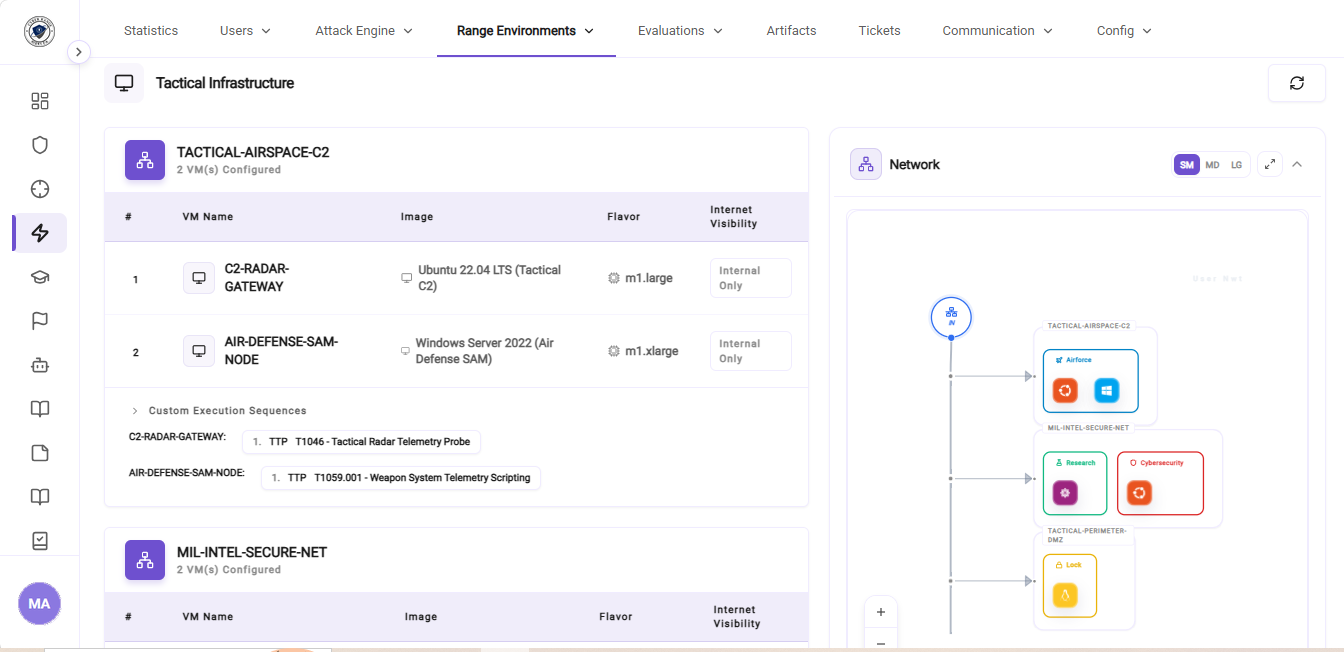
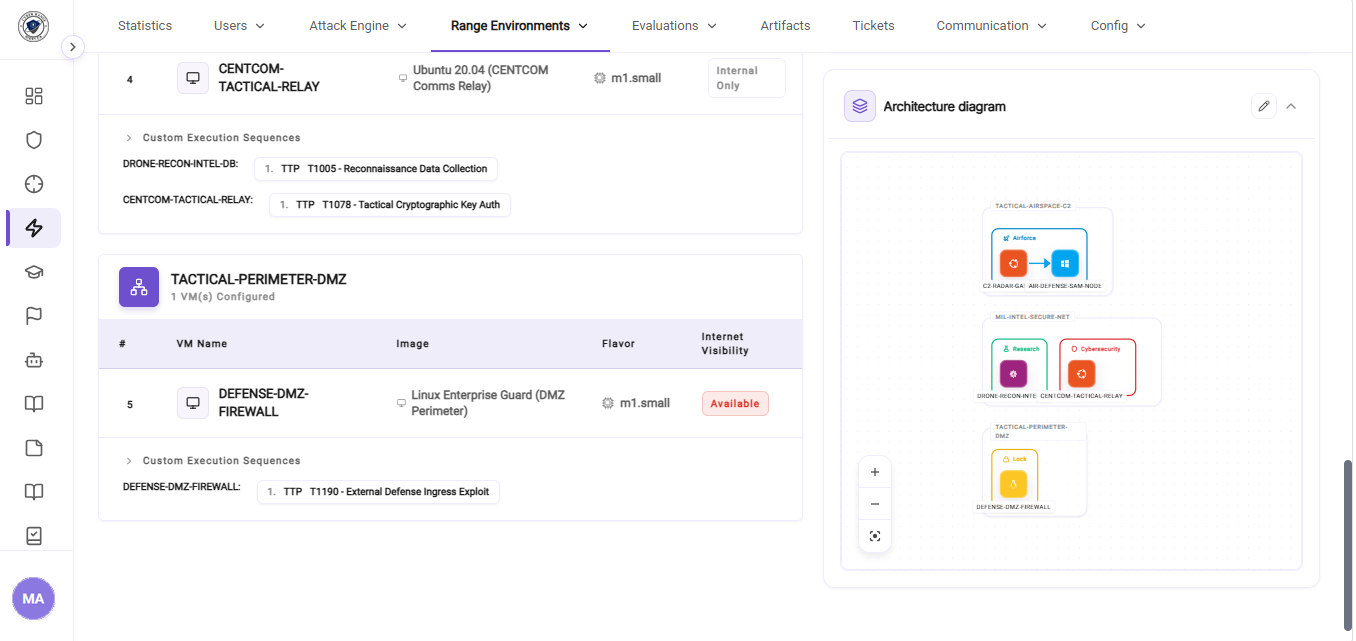
Range: Multi-Machine Network
Full-scale isolated multi-VM enterprise cyber ranges built with interconnected targets, domain controllers, and firewalls.
Asset & Attack VMs Pre-Installed
Dedicated Kali attack VMs and SOC asset workstations equipped with Wazuh, Suricata, Nmap, and DFIR toolkits.
Bridge the Gap Between Offensive Impact and Defensive Readiness
Traditional vulnerability scans and tabletop reviews cannot prove if your SOC will detect an active adversary before domain dominance occurs. Hacktify’s Red-Blue Teaming Platform immerses defenders in high-tempo engagements where every alert matters. Validate your SIEM rules, test EDR containment workflows, and train analysts against unpredictable human attackers in controlled, high-fidelity corporate networks.
Multi-Vector Simulation Scenarios & Exercise Tracks
Curated offensive-defensive battlefields modeled after real-world breaches and modern enterprise threat vectors:
Asset VM with Pre-Installed Cyber Tools
Pre-configured virtual environments loaded with essential security tools including Kali Linux, Suricata IDS, Wazuh SIEM, Nmap, and forensic analyzers.
Ticket Management System
Integrated incident ticketing to coordinate SOC workflows, manage alert investigations, and synchronize team defense drills.
Incident Reporting & Red Team Reports
Standardized reporting pipelines enabling Red teams to detail attack chains and Blue teams to submit formal incident response debriefs.
Attack Detection & Auto-Scoring Mechanism
Intelligent auto-scoring mechanism: when blue team detects attacks, score is auto-detected from defensive monitoring logs while red team gains points for successful offensive operations.
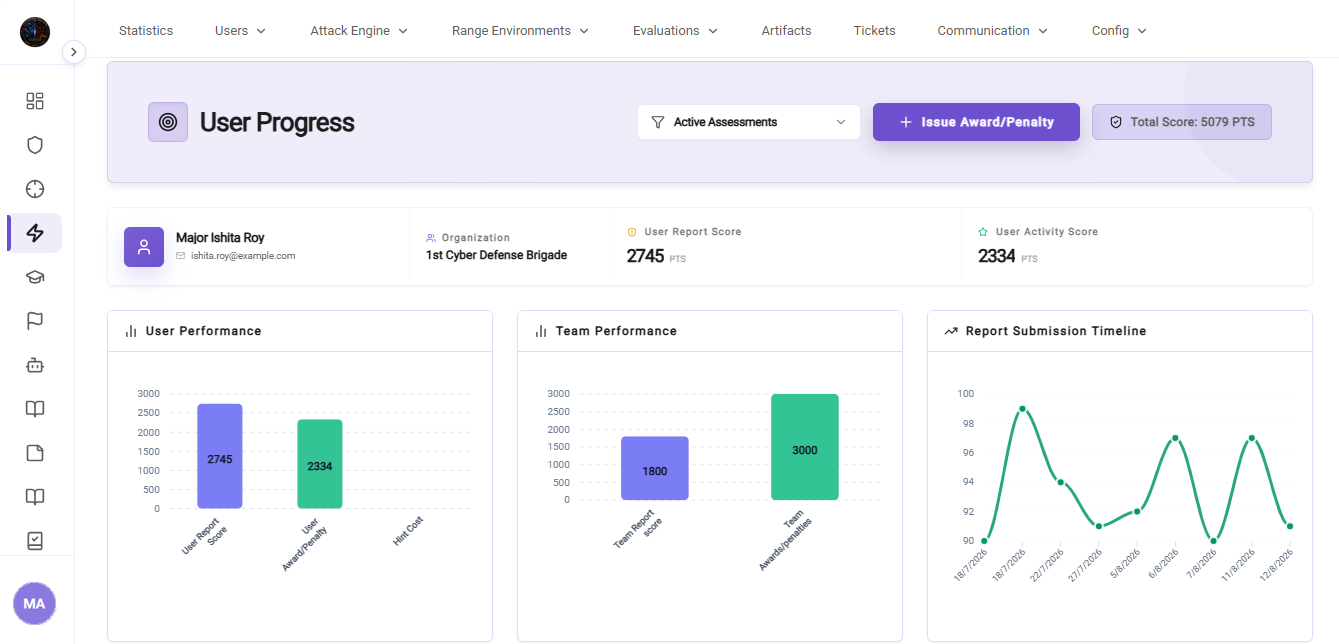
Live Scoring & Telemetry Dashboard
Real-time scoring boards measuring defense detection speed, attack milestones, MTTD, and MTTR operational metrics.
In-Built Chat & Group Collaboration
Participants can chat in real time with exercise organizers and peers, with full support to create custom collaboration groups.
Automated Report Generation
Instant automated generation of audit-grade executive summaries, MITRE ATT&CK coverage heatmaps, and technical debriefs.
Supports Team-Based & Individual Drills
Flexible architecture supporting solo operator drills or multi-squad collaborative Red vs. Blue wargames.
Frontlines Says.