Expert Track

Elite warfare and multi-cloud infrastructure security designed for advanced offensive practitioners: Red Teaming Operations & Adversary Emulation, and Multi-Cloud Security Engineering across AWS, Azure, and GCP.

Expert Track: Elite Red Teaming & Cloud Security Engineering

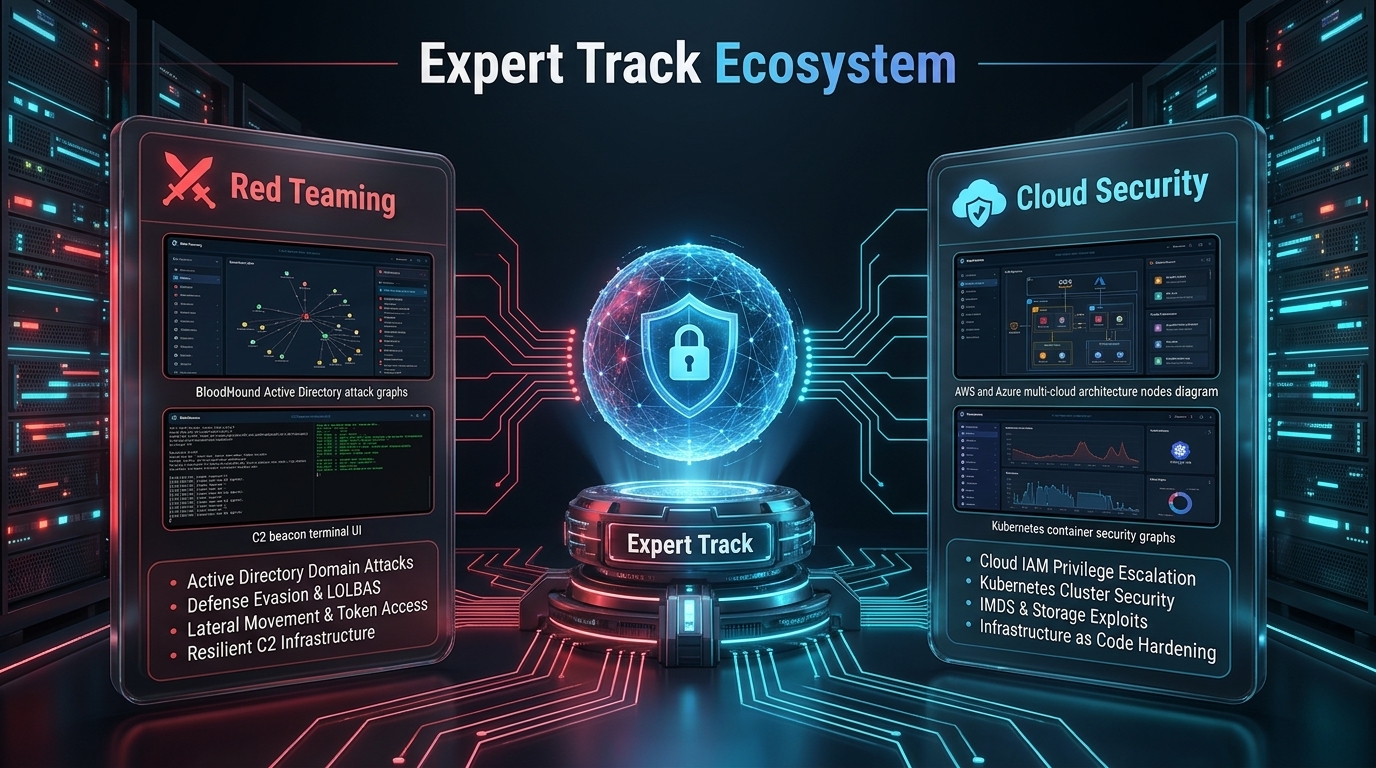
Master advanced adversary simulation, complex enterprise Active Directory compromise chains, and multi-cloud security architecture defense across AWS and Azure.

Adversary Emulation Engagements

Simulate sophisticated threat actors across full-scale corporate enterprise network environments.

Active Directory Domain Compromise

Execute multi-stage domain privilege escalation, token abuse, and credential theft techniques.

Multi-Cloud Infrastructure Audits

Audit IAM policies, cloud metadata services, and storage buckets across AWS and Azure.

Container & Kubernetes Hardening

Identify cluster privilege escalations, container breakouts, and image misconfigurations.

Hacktify Expert Track Red Teaming and Cloud Security Infographic
Hacktify Certified Network Pentester & Red Teaming Operations

Red Teaming Operations

Execute realistic adversary emulation engagements covering enterprise Active Directory attacks, lateral movement, evasion, and persistence.

Active Directory Domain Attacks

Perform Kerberoasting, AS-REP roasting, BloodHound path discovery, and domain escalation.

Defense Evasion & Payload Execution

Bypass modern EDR and endpoint controls using in-memory execution and LOLBAS utilities.

Lateral Movement & Credential Access

Pivot across enterprise network subnets using Pass-the-Hash, token theft, and WMI/WinRM.

Resilient C2 Infrastructure

Deploy multi-tier Command and Control infrastructure with malleable C2 profiles and redirection.

Cloud Security Engineering

Audit, exploit, and harden multi-cloud enterprise environments across AWS and Azure, focusing on IAM permissions and container security.

Cloud IAM & Privilege Escalation

Audit complex IAM policies and trust relationships to uncover lateral escalation vectors.

Container & Kubernetes Security

Test Docker container breakouts, Kubernetes RBAC misconfigurations, and API server policies.

Cloud Metadata & Storage Exploits

Exploit cloud instance metadata endpoints (IMDSv2), exposed S3 buckets, and leaked tokens.

Infrastructure As Code Hardening

Implement automated security guardrails, continuous compliance scanning, and audit baselines.

Hacktify Cloud Security & Infrastructure Pentesting

Frontlines Says.

Reviewed on
4.9
Rated 4.5 out of 5
Contact us

Reach Us for Customized Platform Solutions

We’re happy to answer any questions you may have and help you determine which of our services best fit your needs.

Your benefits:
What happens next?
1

We Schedule a call at your convenience 

2

We do a discovery and consulting meting 

3

Set up Instance for you

Schedule a Free Consultation