Intermediate Track: Mobile Security & Advanced Threat Hunting
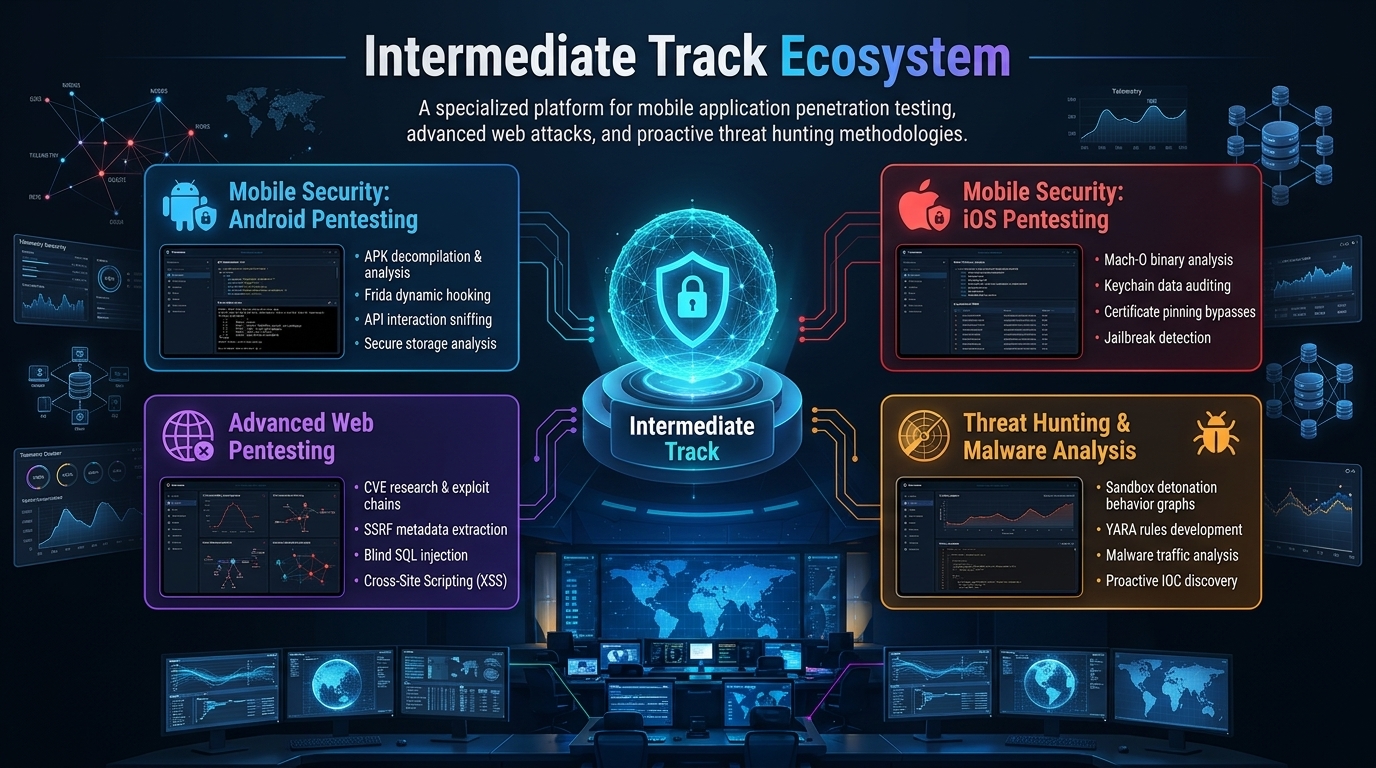
Advance your practical skills with deep dives into mobile application penetration testing, advanced web attacks, and proactive threat hunting methodologies across enterprise networks.
Mobile Reverse Engineering
Decompile, analyze, and modify Android and iOS application binaries directly in browser sandboxes.
Dynamic Runtime Hooking
Intercept app memory, bypass client-side checks, and manipulate live function execution with Frida.
Complex Attack Chains
Execute multi-stage web application vulnerabilities and second-order server exploit paths.
Proactive Threat Hunting
Investigate live network telemetry to detect persistent adversaries before damage occurs.
Mobile Application Security - Android Pentesting
Decompile, analyze, and exploit Android APKs using static audits, runtime hooking, API interception, and local storage reviews.
APK Decompilation & Audits
Reverse engineer Android apps, inspect Manifest files, and find hardcoded credentials with JADX.
Runtime Hooking with Frida
Inject custom scripts to bypass SSL pinning, modify return values, and trace method calls.
Mobile API Traffic Interception
Route mobile application traffic through intercepting proxies to exploit hidden API endpoints.
Root Detection Evasion
Bypass client-side security checks, analyze insecure local databases, and audit IPC components.
Mobile Application Security - iOS Pentesting
Analyze iOS applications across jailbroken and non-jailbroken devices to uncover memory flaws, insecure data storage, and IPC vulnerabilities.
IPA Extraction & Binary Analysis
Inspect Mach-O application binaries, dump classes, and audit application entitlements.
Keychain & Cache Storage Audits
Examine sensitive data leakage in SQLite databases, property lists, and the iOS Keychain.
Runtime Method Swizzling
Hook Objective-C and Swift methods dynamically to bypass authentication and biometric gates.
Jailbreak Detection Bypass
Audit anti-tampering defenses and assess third-party security framework implementations.
Advanced Web Application Pentesting
Take web security beyond basic vulnerabilities with complex exploit chains, second-order injections, and modern framework security flaws.
CVE Discovery & Modern Exploits
Analyze and reproduce real-world CVEs, prototype pollution, and modern web vulnerabilities.
Advanced Server-Side Injections
Chain Server-Side Template Injection (SSTI), blind SQLi, and Remote Code Execution (RCE).
Server-Side Request Forgery (SSRF)
Exploit internal cloud metadata endpoints (IMDS), intranet services, and webhook handlers.
API & GraphQL Security Testing
Audit REST and GraphQL APIs for Broken Object-Level Authorization (BOLA) and logic flaws.
Threat Hunting & Malware Analysis
Proactively hunt stealthy adversaries inside enterprise networks and safely dissect malicious files to extract actionable threat indicators.
Behavioral Sandbox Analysis
Detonate suspicious binaries in isolated virtual sandboxes to observe dynamic process activity.
Malware TTPs & Evasion Dissection
Unpack and analyze obfuscated payloads, scheduled persistence tasks, and memory injections.
Network Threat Hunting
Detect C2 beaconing patterns, suspicious DNS tunneling requests, and covert exfiltration.
Threat Indicator & YARA Generation
Extract actionable IOCs, build custom YARA rules, and update defensive monitoring baselines.
Frontlines Says.